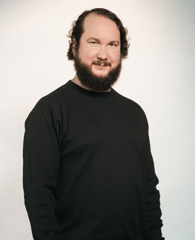
At Sicra, Bjørn analyzes security threats, assesses risks, and contributes to effective incident response. He is particularly focused on understanding which threats pose a genuine risk to customers and which security measures work in practice.
What are you most passionate about professionally?
I'm particularly interested in incident response, threat detection, and cloud security. I really enjoy understanding how attacks unfold in practice, how they can be detected early, and how organizations can build greater resilience over time.
At the same time, I believe security work needs to be practical and operational. Even the best strategies are of little use if you cannot respond effectively when an incident occurs.
What makes a good SOC service?
A good SOC service depends on more than technology and monitoring. It takes people who understand the customer's environment, the threat landscape, and what actually requires a response.
The best SOC teams combine technology, analysis, and experience with clear processes and effective communication. The goal is to detect incidents and help organizations make the right decisions quickly.
You have experience in incident response, pentesting, and security operations. What does that bring to your work?
It gives me a broad understanding of both the offensive and defensive sides of cybersecurity. I've worked on everything from penetration testing and vulnerability assessments to responding to full-scale ransomware incidents.
That makes it easier to understand how attackers think while also knowing which measures actually work when an incident occurs.
What do you see as the biggest challenge organizations face today?
Complexity and pace. Organizations have more systems, more integrations, and larger attack surfaces than ever before, while threat actors are becoming increasingly professional.
Many organizations have invested in a lot of security technology but lack the capacity and expertise to use it effectively. That's why strong security operations and incident response capabilities are so important.
You previously worked on securing Norway's election systems. What was that like?
That may have been the most meaningful job I've ever had. We were protecting one of the foundations of Norwegian democracy, and that came with a profound sense of responsibility and purpose. It also taught me how important resilience, structure, and trust are in security work.
What makes a strong security team?
A strong security team consists of people who are curious, structured, and good at collaborating. No one can handle complex security incidents alone. It's also important to have a culture where people share experiences and learn from incidents instead of hiding mistakes.
What do you want customers to experience when they work with Sicra?
I want customers to see us as pragmatic, accessible, and solution-oriented. We should do more than deliver technology. We should help customers reduce risk and handle security incidents effectively.
What motivates you in your work?
I really enjoy solving complex problems and working systematically through challenges until they're resolved. There's something satisfying about digging deep, understanding what happened, and helping customers return to normal operations.
What's something people might not know about you?
When I do have free time, it often involves some classic nerding out. I'm a big fan of Dungeons & Dragons and really enjoy how games like that combine strategy, teamwork, and creative problem-solving.
I actually think it has more in common with cybersecurity than people might expect. You need to understand your surroundings, collaborate effectively, and be prepared for things not to go according to plan.